
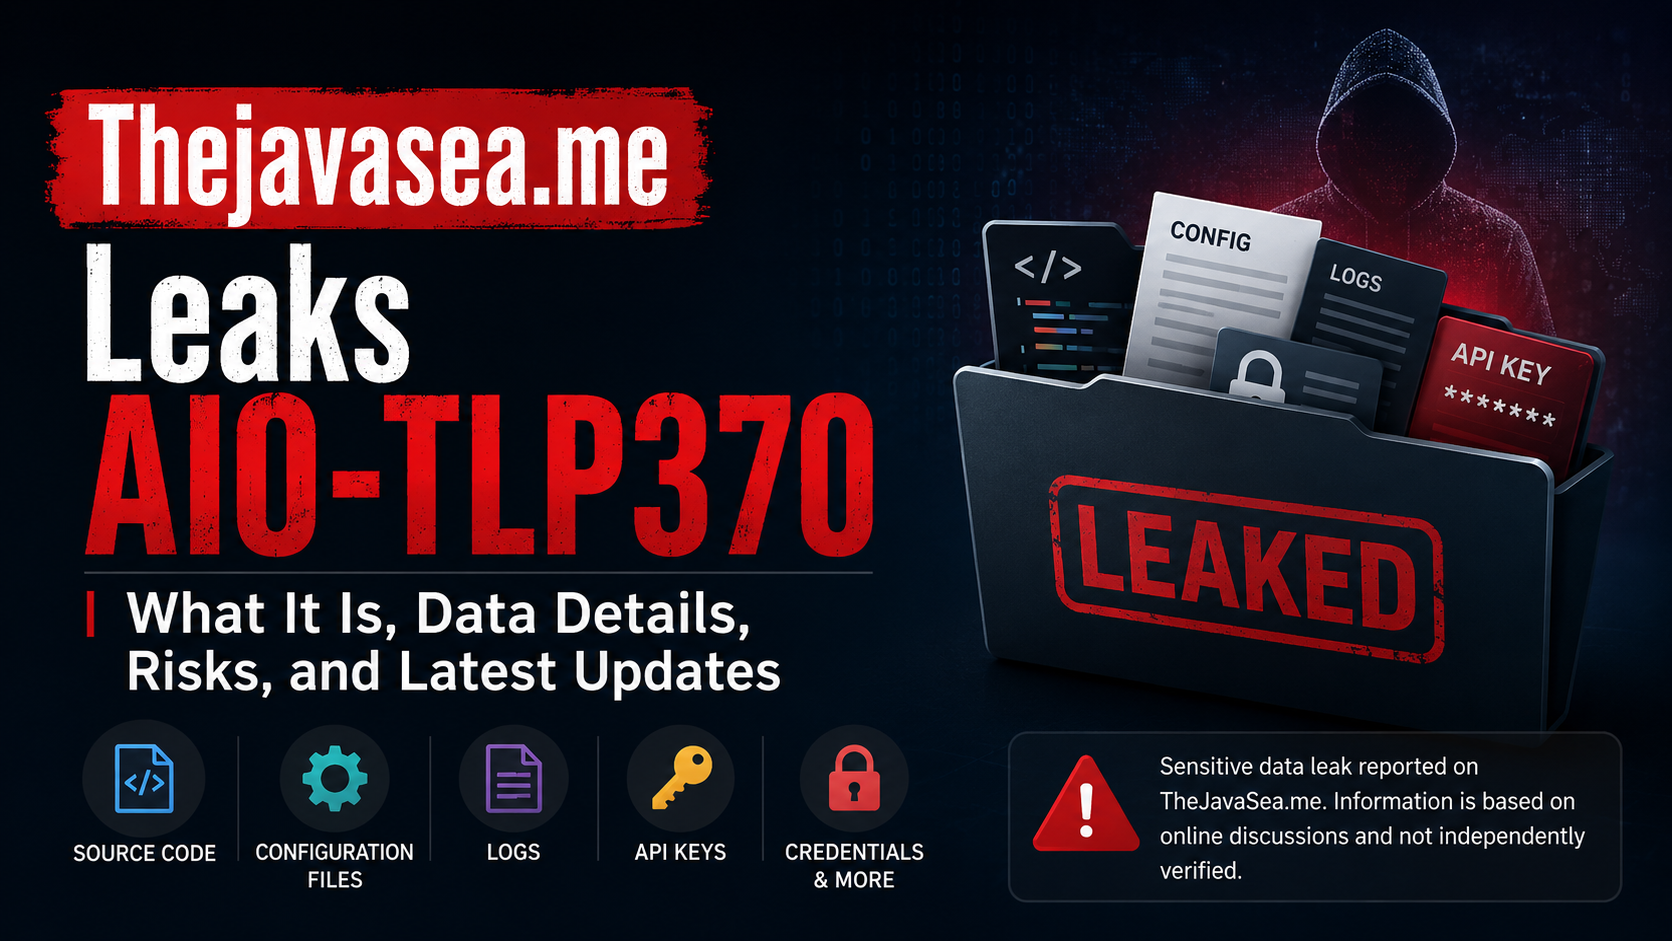
The AIO-TLP370 leak refers to an archive of data that was shared via TheJavaSea.me, a forum known for leaked content. It is reported to contain sensitive materials such as source code, configuration files, logs, API keys, and other credentials. Experts note that this incident is largely described in online discussions, but much of the information has not been independently verified.
What the AIO-TLP370 Leak Is
AIO-TLP370 is described online as an “All-In-One” archive of leaked data associated with TheJavaSea.me. In these contexts, “AIO” often means a combined dataset drawn from multiple sources. The term “TLP370” appears to be just an identifying tag and is not related to any official Traffic Light Protocol classification. According to published accounts, the leak surfaced quietly on tech forums, and some analysts speculate it may have come from a security breach or a disgruntled insider on the site. Once posted, the files were quickly spread across social media and forums. For example, one industry summary notes the leak contains items like source code and thousands of sensitive items (API keys, credentials). At this time, no official confirmation or press release has been made by TheJavaSea or any affected party.
Data Exposed in the AIO-TLP370 Leak
Reports suggest the AIO-TLP370 archive includes several categories of sensitive data. The following list summarizes the types of information said to be in the leak:
- Credentials: Usernames, password hashes and email addresses are often part of these packages. Exposed credentials are very dangerous if users reuse passwords across sites.
- Personal Information: Leaked files may contain personal details like names, phone numbers, and addresses. Such data can facilitate identity theft or targeted phishing campaigns.
- Technical Assets: The archive reportedly contains source code, configuration files, and internal documentation. For example, one analysis listed source code and proprietary configuration appendices as part of a 1.2GB leak file. Exposed code and configuration can reveal system logic and security settings to attackers.
- API Keys and Secrets: Access tokens, API keys and other authentication secrets are highlighted as included items. These may be for cloud services or enterprise platforms. Compromised API keys can grant attackers direct access to protected systems if not revoked.
In one report, an archive named aio-tlpfullv7.3.zip (about 1.2 GB) was said to have appeared in March 2025, containing the items above along with developer notes and incident response playbooks. However, such detailed claims have not been publicly confirmed by independent investigators or the original source. Security analysts caution that even if files with those names exist, they should be treated carefully and verified before assuming they are new or valid breach data.
Security and Privacy Risks
Any leak of this kind poses serious risks for both individuals and organizations. Key dangers include:
- Malware and Scams: Websites that share leaked content often carry malware. Visiting or downloading files from a leak archive can infect devices with viruses, ransomware or spyware. Many security experts warn that links to such leaks can lead to fraudulent download prompts or credential-stealing sites.
- Compromised Credentials: If the AIO-TLP370 archive includes user passwords or API tokens, attackers can use them to hijack accounts and services. Even outdated or unused keys can help cybercriminals understand security patterns and find new vulnerabilities. Publicly leaked secrets often lead to targeted account takeovers and automated attacks on related systems.
- Code and Configuration Exposure: Revealing source code and system configurations makes it easier for attackers to spot weaknesses. Security researchers explain that leaked code can be analyzed to discover unpatched flaws or logic errors. For enterprises, this means attackers can reverse-engineer systems, craft exploit tools more quickly, and launch precise attacks on those systems.
- Privacy and Identity Theft: Personal data from leaks can be used to craft believable phishing emails or identity fraud schemes. Even bits of exposed information (names or addresses) can help attackers impersonate users or bypass some security checks. Organizations must assume any personal details in the leak could be misused by criminals.
- Business and Strategic Impact: For companies and developers, leaked internal documents (like escalation playbooks or design notes) can undermine security policies and response plans. Leaks of operational details may also affect supply-chain trust; partners and customers could lose confidence if a vendor’s systems were exposed. In highly regulated industries, a leak of sensitive data can trigger legal issues, although no specific legal action related to AIO-TLP370 has been reported yet.
In summary, the combination of exposed credentials, technical details, and personal information can significantly raise the threat level for anyone touched by this leak. Even if an individual is not directly affected, security experts advise practicing good cyber hygiene—using unique passwords, enabling two-factor authentication, and monitoring account activity—as protective measures.
If you receive unexpected calls or messages after a data leak, it is important to verify the source before sharing any personal information. Knowing the correct Contact Number Durostech can help users reach the official support team and avoid scams that use fake customer service numbers.
Verification and Uncertainty
Importantly, analysts stress that not all claims about AIO-TLP370 may be accurate. A critical examination of available information shows that many details are based on speculation or repeated rumors. One cybersecurity blog notes that while the phrase “AIO-TLP370” is widely discussed, there is “limited independently verified evidence” about what the leak actually contains or who is affected. In modern cyber incidents, it is common for hackers to repackage old breached data under a new name. That means a so-called “new” leak may include some information that has been exposed elsewhere before. Baddiehu’s analysis warns that duplicate records and recycled data often muddy the picture, making it hard to tell if a breach is fresh or not.
Because of this uncertainty, security professionals advise treating the AIO-TLP370 reports with caution. For example, Baddiehu’s FAQ emphasizes that “many details remain difficult to independently verify” and that public claims should not be taken at face value. No official statement or investigation report has confirmed that the archive is authentic or new. In short, while the leak is being circulated as a data package, defenders should look at the type of information exposed (credentials, code, etc.) rather than the name “AIO-TLP370” itself. The practical advice remains the same: assume any leaked credentials might already be in the hands of criminals, rotate sensitive keys, and monitor systems closely.
Recent Developments and Updates
As of mid-2026, the AIO-TLP370 incident has been covered mostly in blogs and social media rather than mainstream news. Cybersecurity news outlets have noted that the leak became “one of the most talked-about digital leak incidents” in that period. For example, the NewsForPublic site published an overview in May 2026 discussing what happened and why it matters. Around the same time, a tech blog (GPFBalanceCheck) released a general guide warning readers about the risks of “leak-based” websites, using AIO-TLP370 as an example.
In June 2026, more analytical articles appeared. Baddiehu published a fact-check that separates verified points from rumors. TechyFlavors and other tech blogs also added commentary; one such article even claimed a specific March 2025 leak event (the aio-tlpfullv7.3.zip archive) and listed files allegedly in it. These articles underscore the impact: organizations are advised to review any use of AIO-TLP systems and secure exposed credentials.
Importantly, no new confirmed information has emerged recently. No company or official body has announced a breach of that name. Security advisories, if any, have not cited AIO-TLP370 directly. The story remains driven by independent researchers and forum discussions. Individuals concerned about potential impact should continue to follow trustworthy sources. For example, updates may appear on security blogs or RSS feeds where analysts track leaked data trends.
Cybersecurity stories continue to change as new information becomes available. Following trusted technology news platforms like Techoldnewz.in can help readers stay informed about data breaches, security updates, privacy risks, and other important developments.
In summary, the AIO-TLP370 topic is currently at the rumor-analysis stage. Cybersecurity professionals recommend monitoring it as part of normal threat intelligence practice, but also emphasize fundamental precautions: change any suspect credentials and ensure systems logging and alerts are up to date. Future developments would likely come from either law enforcement agencies or affected organizations, but as of now the latest updates are those expert discussions and risk warnings circulating in security forums.